Your domain has an SPF record. Anyone can still send as you.
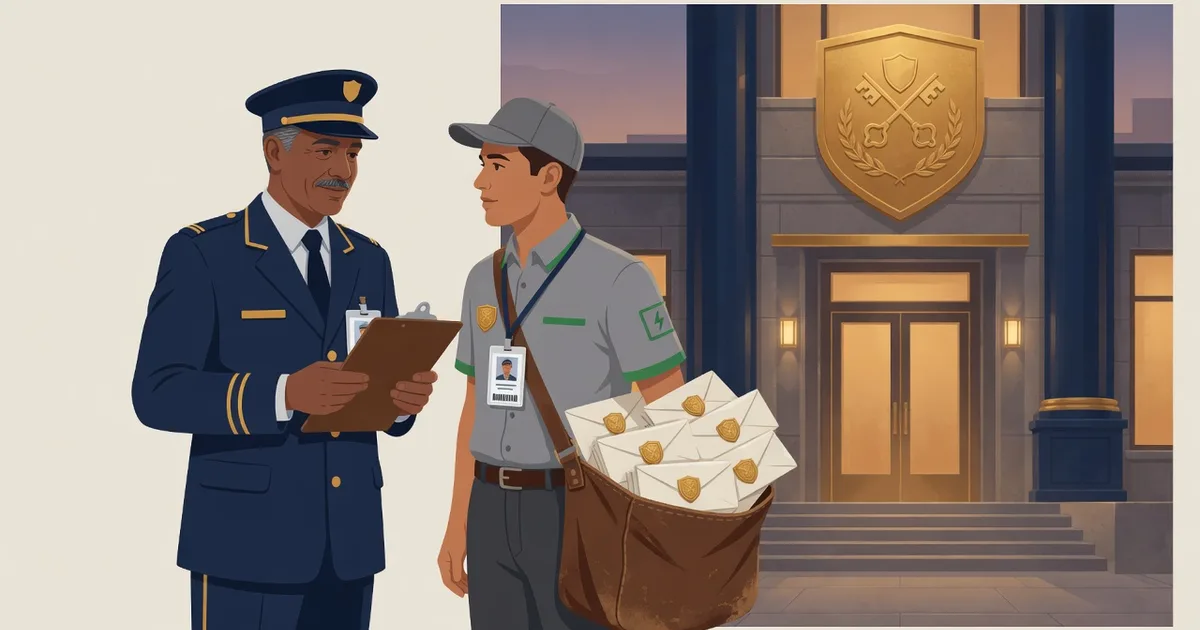
If you only remember one sentence, remember that one.
SPF is the guest list: which servers are allowed to send mail for your domain. It is worth having. It is not the lock.
Here is why. Every email carries two sender addresses. One is on the envelope, used by the mail servers (techies call it the envelope sender, MAIL FROM or Return-Path). The other is the From: line, the only one a human ever sees (the header From). SPF checks the envelope. Your reader checks the From: line. A forger puts their own domain on the envelope, so SPF passes, honestly, for them, and puts your name on the letter inside. SPF saw nothing wrong. Your guest list was never the question.
That is the doorman in the picture above. The courier's badge is real. He just works for someone else, and every letter in his bag carries your crest.
Two more pieces exist. They are usually handed over as a wall of acronyms. They are simpler than that.
DKIM is the seal. Your real server stamps the message. Change the message on the way and the seal breaks. When someone's mailbox automatically forwards your email somewhere else, SPF fails, because the forwarding server is not on your guest list. The seal usually survives, as long as nothing along the way changes the message. Two things often do: mailing lists (they add a footer or a tag to the subject) and anti-spam gateways that add a warning banner. That is why DKIM matters so much: it is often the only check still standing. More on forwarding.
DMARC is the instruction to the server on the other end. It is the only one of the three that looks at the address a person reads, the From: line, and asks whether it matches the guest list or the seal. Then it says what to do when it does not:
p=nonemeans take no action, and maybe send me a report.p=quarantinemeans put it in spam.p=rejectmeans refuse it.
The setting that looks finished
p=none is where most "we did DMARC" projects actually stop. A record is published. Sometimes reports even arrive. The receiving server was told not to block the forgery. Gmail or Microsoft may still junk it on their own, but you are counting on their guess. Your domain can still be spoofed, and the phish goes to your clients, not to you. You hear about it from them.
It is also often the default. A host, a Microsoft 365 setup or a "we configured DMARC" ticket leaves p=none behind, and everyone assumes the job is done. We wrote a whole post on why p=none is more dangerous than it looks.
This is the common case, not a corner. In our 2026 study of 296 Québec organisations, 72% did not block forged email: 24% had no DMARC record or p=none, and another 48% stopped at p=quarantine, one setting short.
It is no longer optional
This is not a best practice you can schedule for next year. Google and Yahoo have required authentication for bulk senders since 2024. Microsoft followed in 2025. Mail that fails does not get a warning. It goes to spam or it is rejected.
A small domain is not exempt from the spoofing half: volume rules decide delivery, they do not decide whether someone can pretend to be you.
One detail that catches people who did set the records up carefully: SPF can pass on your newsletter tool's own domain and still fail DMARC for yours. DMARC is checking the domain in the From: line. A pass on someone else's name does not protect yours.
Monday, in this order
- Send one real message through a checker. Reading the DNS tells you what should happen. The received message tells you what did.
- If there is no DMARC record, or it says
p=none, you are not protected. You are keeping a diary of who is forging you. - Before you move to quarantine or reject, list every system that really sends as you. The newsletter, the website, the copier, Microsoft 365. Reject with one of those missing is how you block your own invoices.
- Then enforce.
noneis the setup phase. It is not the finish.
Pass it on
Did this finally make it click? Someone on your team, or your IT provider, is still sure they are fine because SPF is published. Send them this. It takes three minutes to read and it might save their domain.
If you already knew all of this, you are not the reader. You are the one who forwards it.
Check your own domain free. If a real sender fails, the Email Source Map walks you through that vendor's fix: $99 CAD, one-time, up to 10 sources.
Want to read this later? Email it to yourself.
Stay ahead of email threats
Get our latest DMARC, SPF, and email-security guides in your inbox. No spam — unsubscribe anytime.
We only use your email to send blog updates. One click unsubscribes you.